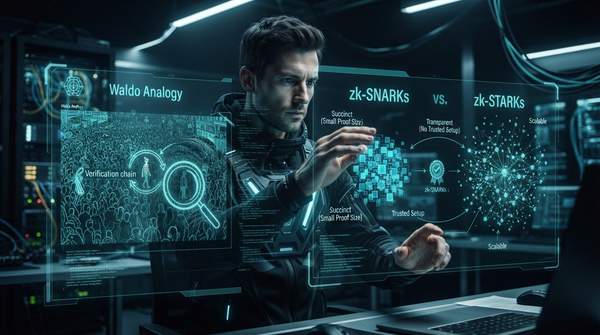
A zero-knowledge proof is a cryptographic method that lets one party — the prover — convince another — the verifier — that a statement is true without revealing anything beyond the fact that it is true. That single sentence carries an unusual amount of engineering weight: it is the reason a blockchain can confirm a transaction is valid without seeing its amount, and the reason a server can verify a credential without reading the data behind it. The concept rests on three formal properties, and in practice it splits into two dominant families, zk-SNARKs and zk-STARKs, whose trade-offs in proof size, verification time, and trusted setup determine which one a project should actually choose.
The Core Idea: Finding Waldo Without Showing Where He Is
The most durable intuition for zero-knowledge proofs is the "Where's Waldo" analogy. Imagine you claim to know Waldo's location on a crowded page, but you do not want to point at him. You could cut a small hole in a piece of cardboard, place it over the page so only Waldo's image shows through, and hand it to your skeptical friend. Your friend can see Waldo — and therefore believes you — but learns nothing about where Waldo sits relative to anything else on the page. The proof convinces; the location stays secret. Ethereum's developer documentation uses this framing to make the point that a proof can be simultaneously convincing and information-free.
Any legitimate zero-knowledge protocol must satisfy three properties, which the blockchain education platform Chainlink and other primary sources enumerate consistently. Completeness means that if the statement is true and both parties follow the protocol honestly, the verifier will be convinced. Soundness means a dishonest prover cannot convince the verifier of a false statement, except with negligible probability. Zero-knowledge means the verifier learns nothing beyond the truth of the statement itself — the cardboard hole, not the page. Together these properties turn "trust me" into "verify me, and learn nothing else."
One further distinction matters before comparing implementations. Early zero-knowledge proofs were interactive, requiring a back-and-forth dialogue between prover and verifier. As Ethereum's documentation explains, non-interactive proving reduces that communication to a single exchange, making proofs more efficient — and, once generated, a proof can be verified by anyone with access to the shared key and the verification algorithm. That breakthrough, the documentation notes, spurred the proving systems used today.
ZKP Type Comparison: Practical Trade-offs
The two leading proving systems are zk-SNARKs (Zero-Knowledge Succinct Non-Interactive Arguments of Knowledge) and zk-STARKs (Zero-Knowledge Scalable Transparent Arguments of Knowledge). A comparative analysis of the two systems, published as a theory-and-practice study on arXiv, identifies them as the two standout frameworks among those developed for zero-knowledge proofs. Their acronyms already announce the trade-off: SNARKs optimize for succinctness, while STARKs optimize for scalability and transparency.
| ZKP Type | Key Characteristic | Proof Size | Verification Time | Trusted Setup Required |
|---|---|---|---|---|
| zk-SNARKs | Succinct and non-interactive; proofs are small | Small — the design goal of "succinct" proofs | Fast, enabled by succinctness | Yes — public parameters must be generated securely in a setup ceremony |
| zk-STARKs | Scalable and transparent; considered quantum-resistant | Larger than most SNARK proofs | Grows only polylogarithmically with computation size | No — relies on publicly verifiable randomness and hash functions |
Reading the table as a decision tool, the rows divide along two axes. The first is proof size versus transparency. zk-SNARKs, per Ethereum's documentation, are defined by being succinct — small enough to be cheap to transmit and verify on-chain — but they require a trusted setup in which public parameters are generated securely. If the parameters are compromised, the compromise undermines the proofs that depend on them, which is why the setup ceremony is treated as a critical security requirement rather than a formality.
zk-STARKs eliminate that requirement entirely. Midnight's technical documentation explains that STARKs rely on publicly verifiable randomness and hash functions rather than elliptic-curve assumptions — which is also, the documentation states, why STARKs are considered quantum-resistant. The price of that transparency is size: STARK proofs are larger than most SNARK proofs. The compensation is in scaling behavior: proving scales quasilinearly with computation size, while verification grows only polylogarithmically, so STARKs, in Midnight's phrasing, "shine on very large computations."
That scaling claim deserves its precision. It is not that STARK verification is always faster than SNARK verification in absolute terms; it is that STARK verification time grows slowly as the underlying computation grows, which is what makes the family attractive for proving large batches of work. For a small statement, a succinct SNARK may remain the more economical choice; for a large one, the polylogarithmic verification curve and the absence of a setup ceremony tilt the decision toward STARKs. The arXiv comparative analysis treats exactly this pairing — Groth16-style SNARKs against STARKs — as the central comparison in the field, which is a signal that practitioners should treat it as the primary decision axis rather than a niche dispute.
Where the Trade-offs Pay Off: Applications
The abstract properties map cleanly onto real deployments. Private transactions are the canonical case: Zcash popularized shielded transfers in which the blockchain verifies a transaction is valid — no double-spending, correct balances — without exposing amounts or participants. Scaling is the second major use: zero-knowledge proofs let a network verify the correctness of a large computation performed off-chain, posting only a compact proof on-chain, which reduces on-chain transaction costs; Ethereum's documentation highlights this as a primary motivation. Identity and credential verification extend the same logic beyond currency — proving you are over 18, or hold a valid license, without disclosing the document itself — and survey literature on arXiv traces applications into finance and healthcare, where proving a property of sensitive data without revealing the data is the entire point.
Notice how the application determines which family fits. A private payment needs a proof that is small and cheap to verify by many independent nodes, which favors the succinctness of SNARKs — provided the project can run a trustworthy setup. A system proving very large computations, or one that cannot tolerate a trusted setup or wants quantum resistance, points toward STARKs, accepting larger proofs in exchange. Midnight's documentation names Starknet, with its Cairo language, as the flagship production deployment of StarkWare's proving stack, showing that the STARK trade-off is not theoretical.
Choosing the Right ZKP for Your Application
Developers and tech enthusiasts should select a ZKP type based on specific application requirements, weighing the trade-offs between proof size, verification time, and the necessity of a trusted setup. In practice the decision reduces to three questions: How large is the computation being proven? Who must verify it, and how expensive is each verification? And can the project responsibly conduct — or afford to avoid — a trusted setup ceremony?
The measurable indicator of a sound choice is that the selected implementation aligns with the project's privacy, scalability, and security goals: zk-SNARKs where compact proofs and fast verification dominate, zk-STARKs where transparency, polylogarithmic verification of large computations, and quantum resistance carry the weight. A team that can answer which of those goals its application actually prioritizes has, in effect, already chosen its proof system.